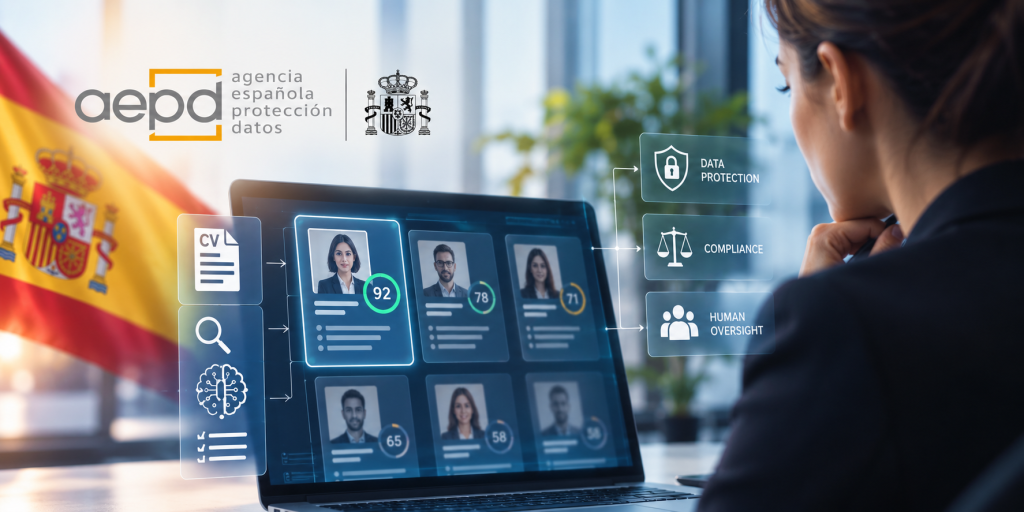
The Spanish Data Protection Agency (AEPD) has issued a preventive warning concerning the planned deployment in Spain of an AI tool intended to support the screening and evaluation of candidates in recruitment and internal mobility processes.
The decision, AI-00009-2026, provides important insight into the data protection safeguards that the AEPD expects organisations to consider when introducing AI into employment-related decision-making processes, particularly in relation to data protection by design, risk assessment, transparency and effective human intervention.
Importantly, the AEPD does not suggest that the GDPR prevents organisations from using AI for recruitment or employee management. On the contrary, it expressly recognises that such technologies may improve efficiency and consistency and provide useful support in evaluating candidates. The issue is whether the processing of personal data associated with those systems is designed and implemented with safeguards appropriate to its characteristics and risks.
The AI recruitment system
The case arose after the AEPD received information in January 2026 concerning the proposed implementation of an AI tool for recruitment and internal mobility.
The system was intended to analyse CVs, assign scores according to candidates’ suitability for a particular position and prioritise applications. It could therefore directly influence decisions concerning access to employment and professional progression.
According to the information available to the AEPD, the system had not yet been deployed in Spain, although the company had already provided information regarding its planned implementation. The company explained that the tool was intended to improve the efficiency, consistency and objectivity of the initial assessment of candidates. It would generate a score based on the degree to which a candidate matched the requirements of the position, while the final decision to screen or reject a candidate would remain with a human decision-maker. The company also indicated that the system would exclude the analysis of sensitive attributes and would be subject to periodic audits.
The tool was being developed centrally by the corporate group to which the Spanish company belonged, with the group also analysing its data protection implications. The Spanish entity indicated that it would assess the group’s conclusions and adopt any necessary measures before the system was eventually put into operation.
What is an AEPD preventive warning?
The decision is significant because it is not a finding that the company infringed the GDPR and it does not impose a fine.
Article 58(2)(a) GDPR allows a supervisory authority to issue a warning to a controller or processor where intended processing operations are likely to infringe the GDPR. The AEPD emphasises the preventive nature of this power: it is not necessary for the authority to establish with certainty that the proposed processing will infringe the Regulation.
The purpose is instead to alert the organisation to potential compliance concerns before the processing takes place, allowing it to take those concerns into account and adapt the proposed processing in accordance with the GDPR and the principle of accountability. The AEPD also notes that a warning may be issued even where the information available to the authority is incomplete.
This makes the mechanism particularly relevant in the context of emerging technologies: regulatory intervention does not necessarily have to wait until an AI system has been deployed and an infringement has occurred.
The GDPR does not prohibit AI recruitment tools
One of the most relevant aspects of the decision is the AEPD’s recognition that the GDPR does not prevent the use of AI technologies in recruitment and employee management.
The AEPD acknowledges that AI tools can improve efficiency and consistency and assist organisations in assessing candidates. Properly designed and used, they may also contribute to improving the effectiveness and quality of certain data processing activities and the inferences derived from them.
The requirement is that the processing of personal data takes place with safeguards appropriate to the nature and risks of the system. According to the AEPD, those safeguards should be incorporated into the design, evaluation, selection, configuration and implementation of the technology itself.
Data protection by design and risk assessment
The AEPD places particular emphasis on data protection by design and by default under Article 25 GDPR.
Data protection principles and safeguards should therefore be integrated from the initial stages of a technology project, including the design, evaluation, selection, configuration and implementation of the system. This approach should enable organisations to identify the risks associated with the processing and implement appropriate measures to address them. Risk management must also continue throughout the lifecycle of the processing.
Where, having regard to the nature, scope, context or purposes of the processing, the proposed processing is likely to result in a high risk to individuals’ rights and freedoms, the organisation must conduct a data protection impact assessment (DPIA) before the processing begins, in accordance with Article 35 GDPR.
Transparency towards candidates and employees
The AEPD also highlights transparency as a particularly important consideration where an AI system evaluates candidates and assigns scores concerning their suitability for a position.
Under Articles 12 to 14 GDPR, candidates and employees must receive clear, accessible and comprehensible information concerning the processing of their personal data. This includes information about the purposes of the processing and the role played by the AI tool in the evaluation process, to the extent required in the particular circumstances.
Where the conditions for automated decision-making under Article 22 GDPR are met, the specific information requirements under Articles 13(2)(f) and 14(2)(g) GDPR also apply.
Human intervention must be effective
The company’s position that the final decision would always be made by a human was relevant, but the AEPD makes clear that the existence of a human decision-maker is not necessarily sufficient.
Under Article 22 GDPR, individuals have the right, subject to the exceptions and safeguards established by the Regulation, not to be subject to decisions based solely on automated processing, including profiling, which produce legal effects or similarly significantly affect them.
The AEPD therefore emphasises that human intervention must be effective in practice. The person making the decision must be capable of critically assessing the information or score generated by the AI system and reaching the relevant decision without being effectively determined by the automated output.
Whether Article 22 applies must consequently be assessed by examining how the decision-making process actually operates, rather than simply whether a human formally appears at the end of the process.
What does the AEPD require?
In its formal warning, the AEPD states that, when evaluating and potentially implementing the AI recruitment tool, the company must comply with its obligations concerning data protection by design and by default and adopt appropriate technical and organisational measures to ensure and demonstrate compliance with data protection law.
In particular, the company must assess the risks that the processing may create for candidates and employees and, where the processing is likely to result in a high risk within the meaning of Article 35 GDPR, conduct a DPIA before processing begins.
It must also ensure compliance with the principle of transparency and, taking into account the actual functioning of the system and the degree of human involvement in the decision-making process, determine whether Article 22 GDPR applies and, where it does, comply with the limitations and safeguards established by that provision.
The AEPD further warns that failure to adopt any measures necessary to bring the proposed processing into compliance could result in an infringement and potentially lead to further investigative or corrective action, including sanctions.
Conclusion
The AEPD’s warning reinforces the importance of addressing data protection compliance before an AI system is deployed, rather than only after its implementation.
For organisations considering AI systems for recruitment, candidate screening, internal mobility or other employment-related decisions, the decision highlights four particularly important considerations: integrating data protection into the design and implementation of the system, assessing risks and determining whether a DPIA is required, providing meaningful transparency to affected individuals, and ensuring that any claimed human oversight is effective in practice.
At the same time, the AEPD adopts a balanced approach. It does not treat the use of AI in recruitment as inherently incompatible with the GDPR. Rather, it recognises the potential benefits of these technologies while requiring organisations to demonstrate that their use is accompanied by safeguards proportionate to the risks they create.
For companies deploying AI in employment-related processes, AI-00009-2026 therefore provides an important early indication of how the AEPD expects the GDPR’s existing principles to be applied to AI-assisted decision-making in practice.